A single bug in smart contract development can result in millions of dollars being drained in minutes. Smart contracts are self-executing programmes on the blockchain that run when predefined conditions are met. Development shops charge between $7,000 to $45,000 to create and deploy a smart contract, but the cost of poor security can be devastating. Many developers focus on functionality and overlook security vulnerabilities that matter. This piece gets into common security mistakes developers make, from reentrancy attacks to poor access control, and explores smart contract development tools and best practises to protect against these errors.
What Is a Smart Contract and Why Security Matters
Self-Executing Code on the Blockchain
Smart contracts are self-executing programmes that run on blockchain platforms and enforce predefined rules and conditions on their own. These digital agreements work through simple “if/when…then…” statements written into code on a blockchain. A network of computers executes the actions on its own at the time predetermined conditions are met and verified. These actions might include releasing funds or registering assets. The blockchain gets updated after the transaction completes, and the transaction cannot be changed.
Traditional contracts rely on intermediaries and legal enforcement. Smart contracts eliminate the need for third parties to make actions easier between parties. The agreement lives as code deployed to a blockchain, and every node stores a copy. The contract executes itself after the coded conditions are satisfied, and the outcome is recorded for good.
Immutability Creates Permanent Vulnerabilities
Ethereum smart contracts are designed to be immutable after deployment to the blockchain. This immutability provides reliable execution logic and makes audit trails possible for transparent interactions. But immutability conflicts with the reality of software development, where bugs need fixing and security vulnerabilities require patching.
Any flaw embedded in contract logic can persist indefinitely. The contract code becomes part of the blockchain after deployment, and blockchain history is designed to be difficult to change. This means no quick fixes, no hotfixes at midnight, and no rollbacks. A typo in token economics cannot be corrected, and attackers can exploit a reentrancy vulnerability before anyone patches it. Smart contracts are deployed on an immutable blockchain, so any coding errors or vulnerabilities become permanent and make them susceptible to various attack vectors.
Financial Losses from Security Flaws
The cost of these permanent vulnerabilities has proven catastrophic. The 2016 DAO hack drained over AUD 76.45 million, and the 2017 Parity wallet freeze locked AUD 428.12 million for good. According to data from the Defillama hacks page, a staggering AUD 13.82 billion has been stolen from DeFi platforms due to various smart contract vulnerabilities. Smart contract exploits led to almost AUD 68.80 million in losses across 16 incidents during Q1 2024 alone, averaging AUD 4.28 million per exploit.
Common Security Mistakes During Smart Contract Development
Developers deploy contracts with preventable vulnerabilities that attackers exploit within hours of mainnet launch. Understanding these common security mistakes separates failed projects from those that protect user funds.
Ignoring Reentrancy Attack Vulnerabilities
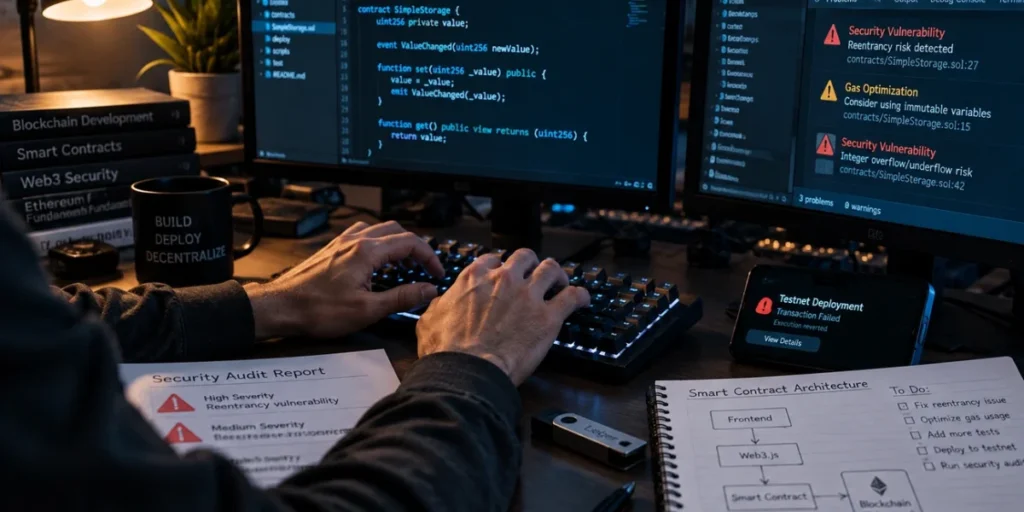
Reentrancy exploits occur when a function makes an external call to another contract before updating its own state. The external contract can call back into the original function and repeat actions like withdrawals using the same state. The 2016 DAO attack drained AUD 91.74 million through this vulnerability. Reentrancy attacks have caused approximately AUD 535.15 million in total losses. Developers must follow the checks-effects-interactions pattern: validate conditions, update internal state, then make external calls.
Poor Access Control Implementation
Missing or poorly implemented access control allows unauthorised users to execute privileged functions. The Balancer V2 exploit in November 2025 resulted in AUD 195.71 million in losses when improper access controls on the manageUserBalance function allowed attackers to bypass protections. Zoth lost AUD 12.84 million when a single compromised deployer wallet enabled malicious contract upgrades. Role-based access control using proven patterns prevents these failures.
Gas Limit Assumptions
Functions requiring more gas than the block gas limit become unexecutable. The GovernMental Ponzi scheme contract became unusable when its creditor array grew too large. This made payout functions impossible to execute and trapped funds forever.
Front-Running Vulnerabilities
Transactions sit visible in the mempool before processing and allow attackers to observe and front-run them with higher gas fees. MEV bots have extracted at least AUD 1.53 billion in profits on Ethereum and BSC. They exploit transparent transaction ordering to manipulate prices and steal value from legitimate users.
Testing and Auditing Mistakes Developers Make
Testing mistakes compound development errors and turn preventable issues into mainnet disasters that drain user funds within hours of deployment.
Skipping Testnet Deployment
Direct mainnet deployment without adequate testnet coverage remains the most common cause of pricey smart contract exploits. Testnets work exactly like Ethereum Mainnet, except they use ether with no real-life value. This allows anyone to interact with contracts without putting funds at risk. Bugs invisible in unit tests become apparent when code runs on a distributed network with independent operators, network latency, and concurrent transactions. A surprising number of exploits involve code deployed directly to mainnet without adequate testnet coverage.
Insufficient Edge Case Testing
Unit testing proves effective minimally to improve smart contract security when used in isolation. Unit tests verify individual functions work as expected, but they only catch errors in the specific tests written. Manual testing can detect edge cases that automated testing tools miss. Many developers skip complete fuzzing and integration testing before deployment.
Relying Only on Automated Security Tools
Automated tools prevented just 8% of attacks in one dataset, amounting to AUD 227.82 million out of AUD 3.52 billion in losses. These tools catch around 65% of common vulnerabilities and leave the critical 35% of business logic and economic exploits for expert human review. 38.1% of auditors do not find security tools useful, which highlights their limitations.
Deploying Without Professional Audits
Professional audits cost between AUD 38,224.76 to AUD 152,899.02 for most DeFi protocols, yet the average loss per smart contract exploit runs well into seven figures. Unaudited contracts expose projects to catastrophic financial loss and immediate reputational collapse. Audits combine manual code review with automated analysis to identify vulnerabilities before immutable deployment.
Smart Contract Development Tools and Security Best Practises
Security tooling and established patterns are the foundations of production-ready smart contract development. Developers who implement these practises reduce their attack surface by a lot before deployment.
Using Solidity Security Patterns
The Checks-Effects-Interactions pattern prevents reentrancy by checking conditions, updating state, and then making external calls. Developers should never use tx.origin for authorisation as it creates phishing vulnerabilities. Using msg.sender instead will give proper caller verification. Always deploy contracts with the latest Solidity compiler version to benefit from recent security patches.
Implementing OpenZeppelin Libraries
OpenZeppelin Contracts provide battle-tested and audited implementations of ERC standards and security patterns. These reusable components minimise risk by using code that has undergone multiple security audits. The library has access control mechanisms, reentrancy guards and safe arithmetic operations. Developers should always install OpenZeppelin from published releases rather than copying source code.
Static Analysis Tools: Slither and Mythril
Slither runs static analysis in seconds and detects vulnerabilities with a false positive rate of just 10.9%. The tool has 76+ built-in detectors for issues like reentrancy and unchecked calls. Mythril uses symbolic execution and SMT solving to explore all execution paths and uncovers complex multi-step vulnerabilities that simpler tools miss.
Formal Verification Methods
Formal verification mathematically proves smart contract correctness across infinite execution scenarios. This technique detects integer overflows, reentrancy and gas optimisation issues that slip past auditors. So formally verified contracts provide stronger guarantees than testing alone.
Bug Bounty Programmes Before Mainnet Launch
Immunefi has paid AUD 214.06M across 650+ protocols, with 93% of critical vulnerability disclosures coming through their platform. Bug bounties provide continuous security scrutiny from independent researchers who identify edge-case vulnerabilities that internal teams overlook.
Conclusion – Smart Contract Development
Smart contract security determines the difference between successful blockchain projects and catastrophic financial losses. Developers must prioritise security from the earliest development stages rather than treating it as an afterthought. Preventable vulnerabilities like reentrancy attacks, poor access control, and unchecked external calls have cost the industry billions. Proven security patterns combined with detailed testing, professional audits, and bug bounty programmes create defence-in-depth that protects user funds before immutable deployment.
Related Article: Fintech Explained: How Technology Is Reshaping Money, Banking, and Payments
What makes smart contracts vulnerable to security attacks?
Smart contracts are vulnerable because they are immutable once deployed to the blockchain. Any coding errors, security flaws, or vulnerabilities become permanent and cannot be patched or fixed after deployment. This means attackers can exploit these weaknesses indefinitely, leading to significant financial losses.
What is a reentrancy attack and why is it dangerous?
A reentrancy attack occurs when a function makes an external call to another contract before updating its own state. The external contract can then call back into the original function repeatedly, allowing actions like withdrawals to be executed multiple times using the same state. This type of vulnerability has caused approximately AUD 535.15 million in total losses.
How much do professional smart contract audits typically cost?
Professional smart contract audits typically cost between AUD 38,224.76 to AUD 152,899.02 for most DeFi protocols. Whilst this may seem expensive, the average loss per smart contract exploit runs well into seven figures, making audits a worthwhile investment before deployment.
Why shouldn’t developers rely solely on automated security tools?
Automated security tools only prevented 8% of attacks in one dataset and catch approximately 65% of common vulnerabilities. They miss critical business logic and economic exploits that require expert human review. This is why 38.1% of auditors do not find security tools useful on their own.